Two Industries. One Problem.
For years, Ralph Pasquariello and Craig Sekowski worked alongside each other as insurance and technology experts. They kept seeing the same disconnect: Cybersecurity spoke in technical terms.Insurance spoke in policy limits.The C-suite needed to understand the financial risk. That gap became CYBERISKIQ.
Behind the 
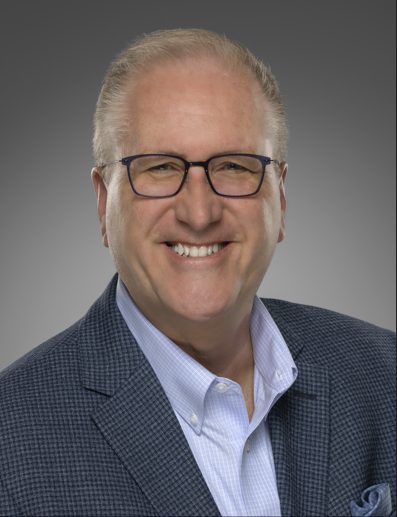
Craig Sekowski
CEO & Co-Founder
With over 30 years of experience spanning IT, cybersecurity, artificial intelligence, and regulatory compliance, Craig is a recognized Industry Cyber Advisory Subject Matter Expert specializing in cyber financial quantitative risk. As Co-Founder and CEO of CYBERISKIQ, he leads the company's mission to translate complex technical threats into clear business impact for Fortune 1000 organizations, giving leadership teams the clarity they need to act before risk becomes crisis. A trusted collaborator with the US Secret Service Cyber Fraud Task Force, Craig brings both public-sector insight and private-sector strategy to every engagement. His mantra guides his work: “Save companies before an incident occurs.”
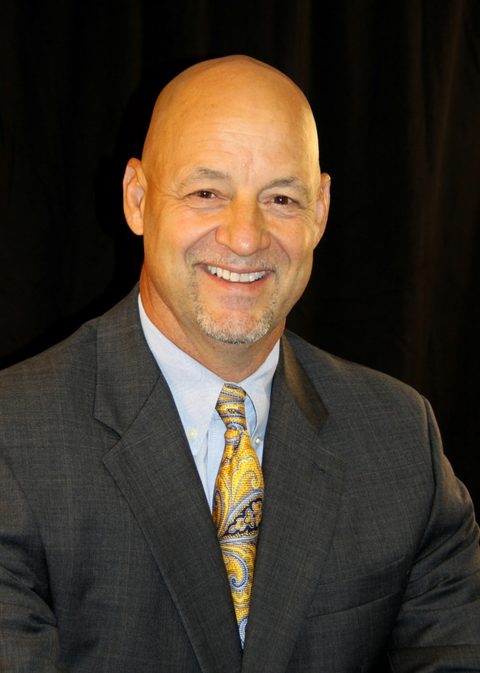
Ralph Pasquariello
Co-Founder, CLCS
25 years in printing, transitioning into commercial insurance for 14 years. A trailblazer specializing in cyber insurance, speaking and moderating at hundreds of events on Cyber exposure for all industries including Operational & Intellectual Technology. Former Executive Committee Chairman for the Tech400, Cyber Symposium and advisor to the Georgia Tech Research Institute. Conference appearances and collaboration with the FBI and US Secret Service Cyber Fraud Task Force. Co-creator CYBERISKIQ's Cyber Business Impact Assessment Report. His Mantra: “What if your wrong?”
Our approach
We help CFOs, CISOs, and CIOs identify cyber insurance coverage gaps using NIST, CIS, and FAIR methodologies - delivered through a Cyber Business Impact Analysis and Financial & Security Risk Quantification. The result is a shared, defensible picture that your leadership team, broker, and IT department can act on together.